Hacklabs Finale Week - Writeup
December 24, 2020
Hi there, this is the writeup for my final week. Join the Discord server (links on HackLabs Instagram account) Click Here. Lets get started ! *note : I’m new in CTF :D

Incremental Crunchy Cracker - Forensics
Given a protected .zip file with some password hint (is digit) and the title is Incremental & Crunchy. Either you can make the wordlist with crunch or crack it straight away with JohnTheRipper.
So i convert the zip into hash with zip2john.

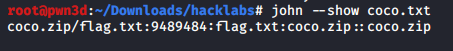
And crack the hash with Incremental mode with John,

I got the password of the zip : 9489484
Extract it with the password, and this is the flag :
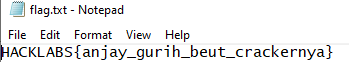
Flag : HACKLABS{anjay_gurih_beut_crackernya}
Marcopolo Exodus - Misc
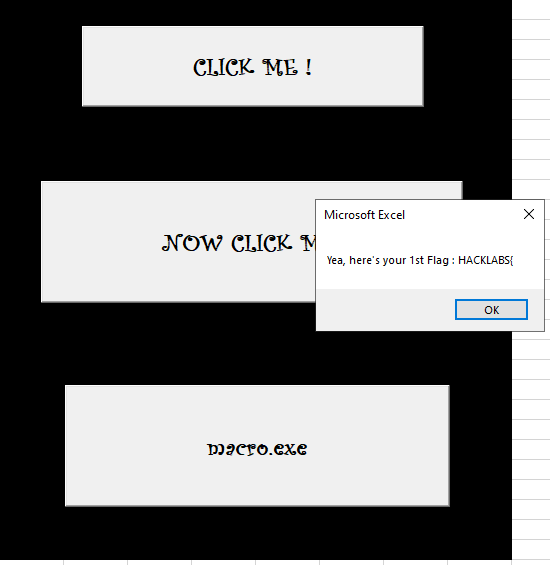
Given .xlsm file with macro inside it, to see the source code of the macro press (alt+f11). When i click the first box it returns the first part of the flag : HACKLABS{, then i click the second box and the macro wants a password but i dont know the password yet.
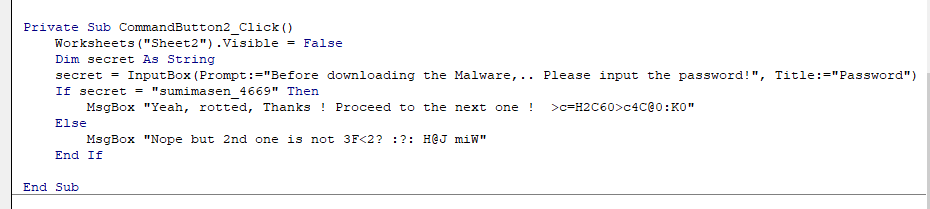
macro source code, password for the second box is : sumimasen_4669. If i input the correct password it will return a “ROTTED” string. Lets try to rotate it with ROT47. The result is : m4lware_m4cro_iz_ and this is the second part of the flag.
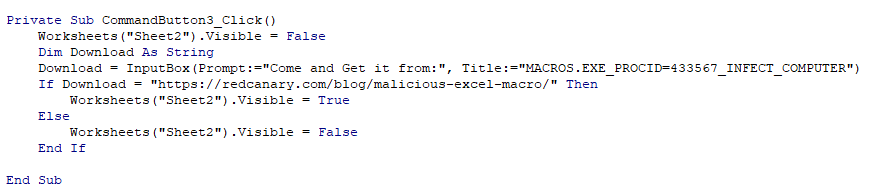
For the last part, macro will request an input from user. If input is true then sheet2 will available.
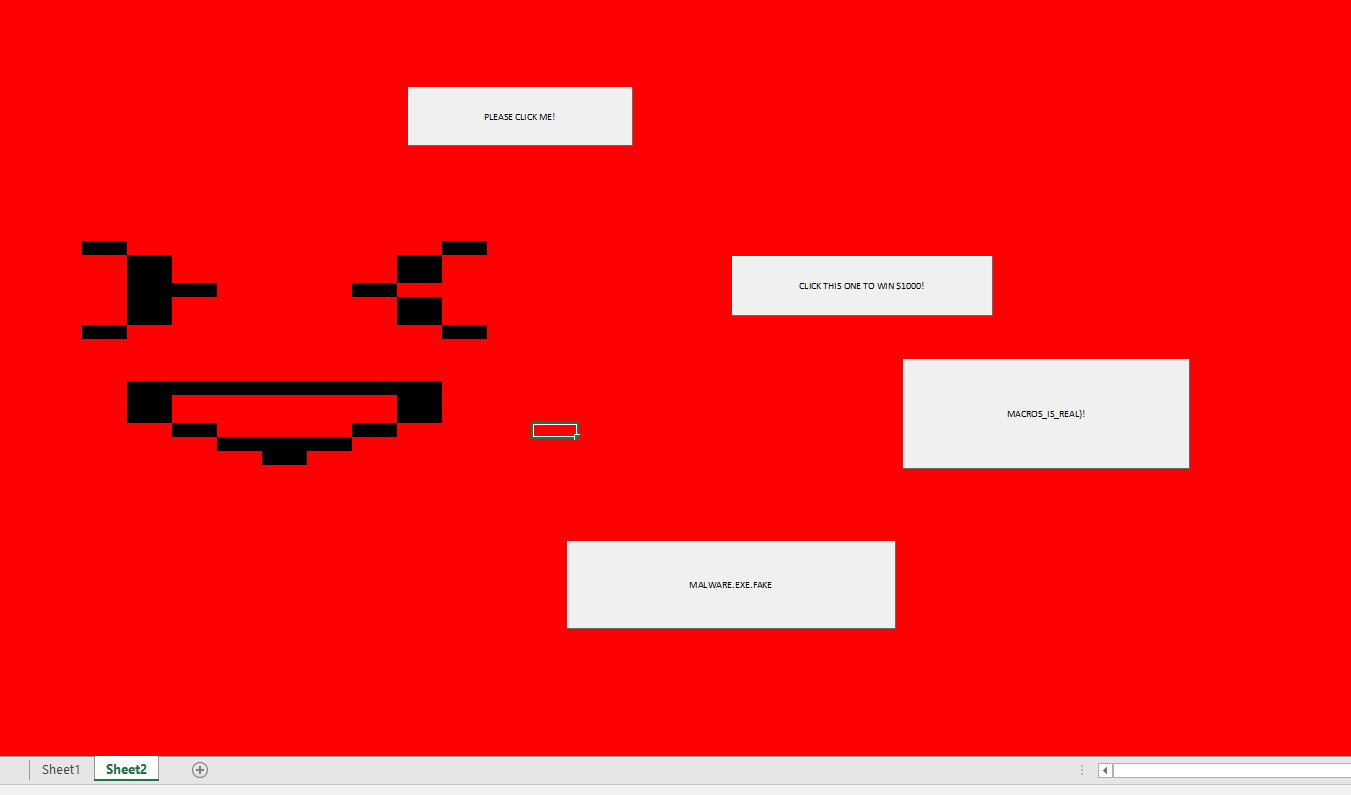
In the sheet2 i can’t find the flag right away. So i just find the “}” because i think the last part of the flag is in sheet2 but it’s hidden.
Last part of the flag :
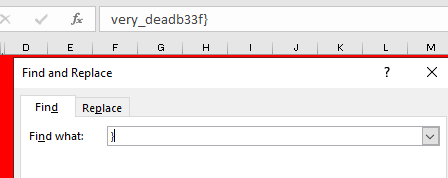
Flag : HACKLABS{m4lware_m4cro_iz_very_deadb33f}
Man’s Best Friend - OSINT
Given a video from Sherpa youtube channel. In this chall i need to find the exact location where the video is taken.
So i took a screenshot and reverse search the image with yandex or google reverse image.
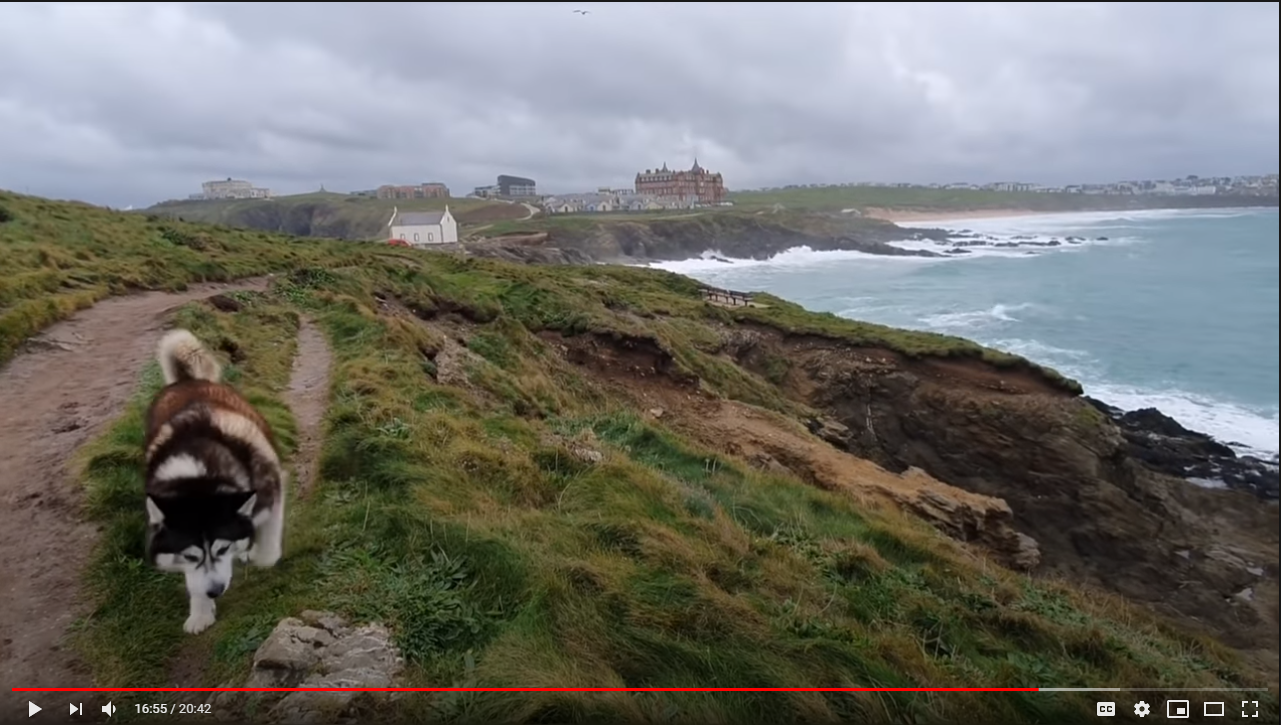
There is a big red building and small white building. I need to find what the name of the building.
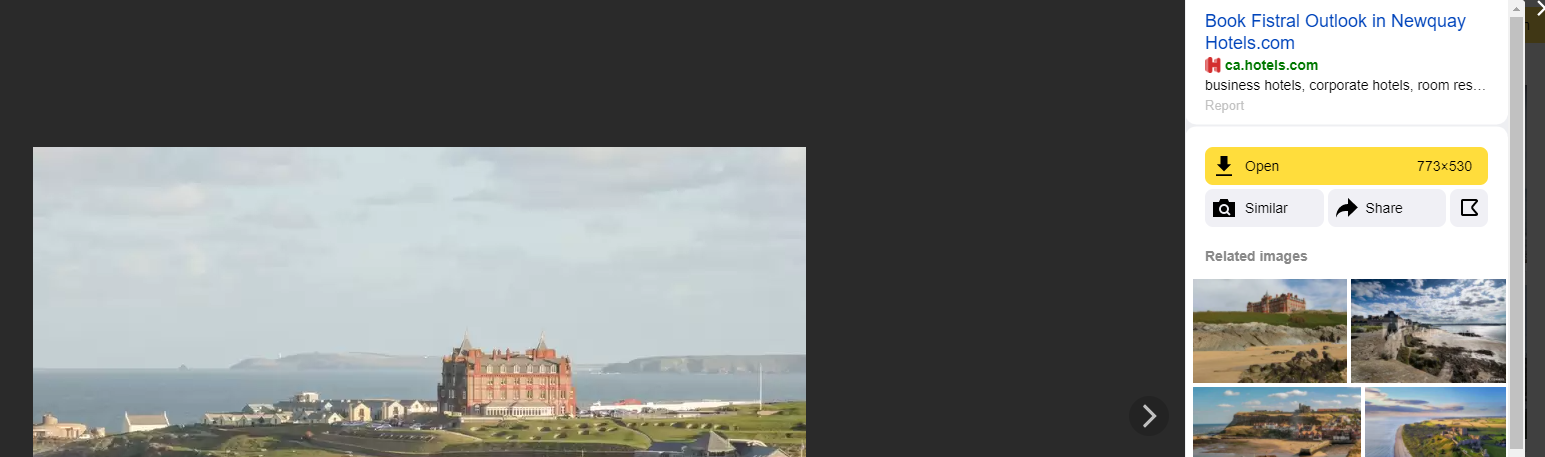
The red building name is Fistral Outlook Hotel. Lets find where is it exactly. I look on google earth (Towan Headland) to see the satelite view and i got the Fistral Outlook Hotel and the white building.
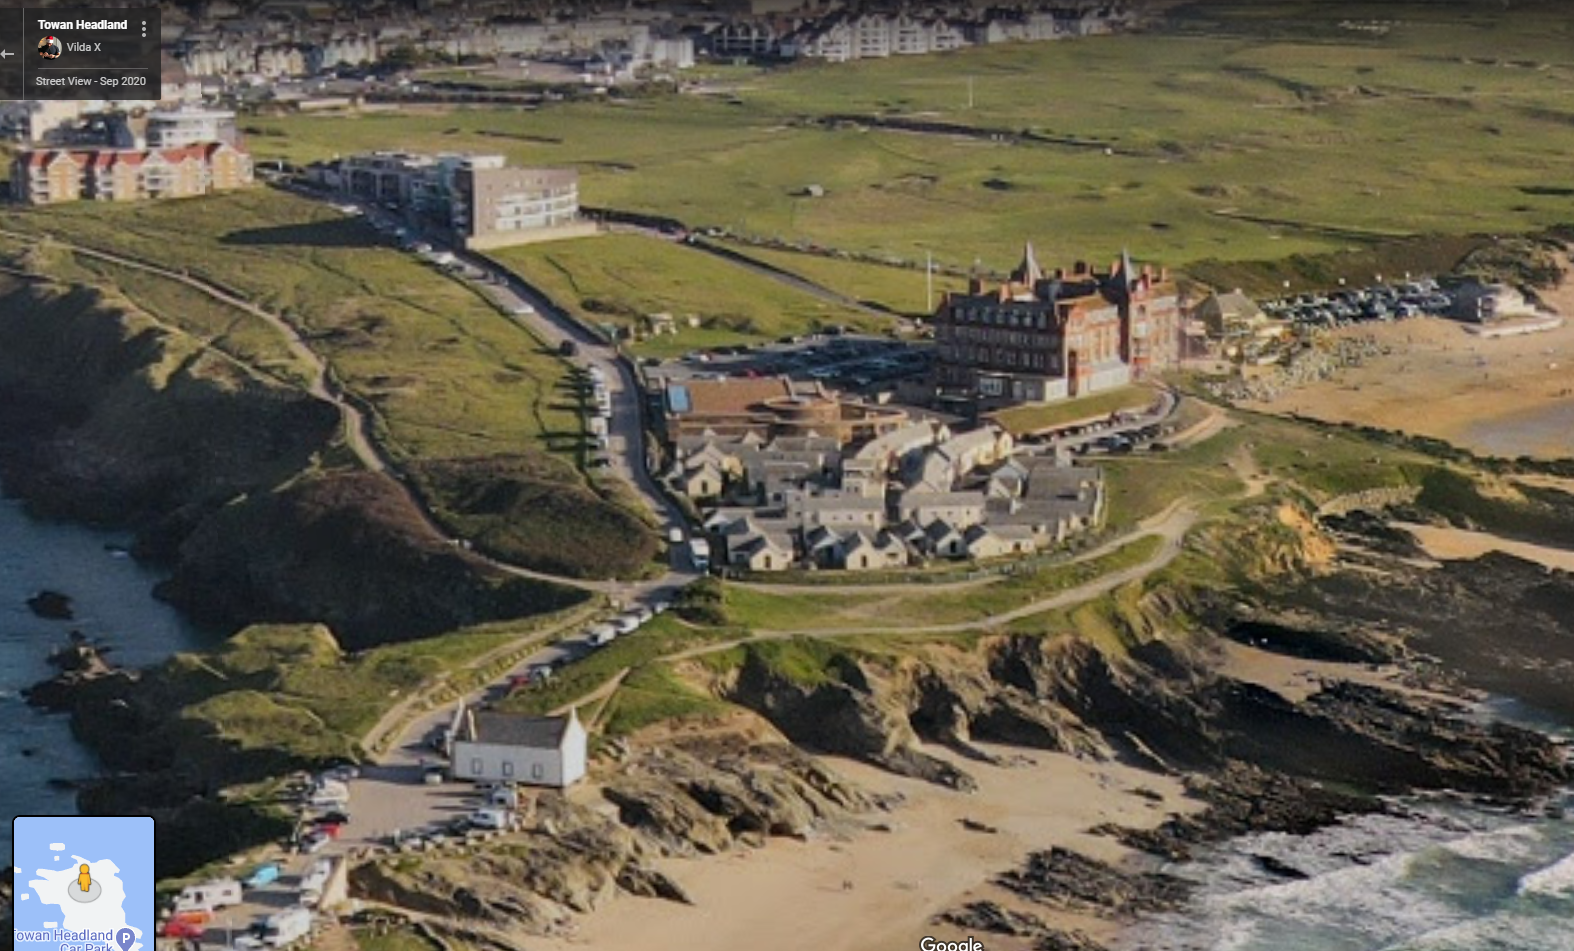
Flag : HACKLABS{Towan_Headland}
17.878.103.347.812.890.625 – Cryptography
Given a encrypted .png image with XOR algorithm. I’ve been stuck in this challenge, but i managed it with some googling how XOR algorithm works.So XOR works like this take an example we want to XOR A with B.
A XOR B = C, and B XOR C = A. So XOR is reversible, right?
I came with some ideas, what if i XOR the correct .png header with the encrypted header ? Based on my previous explanation XOR is reversible.
Encrypted header : 15 5F 43 17 80 60 D1 6B Correct .png header : 89 50 4E 47 0D 0A 1A 0A Result : 9C 0F 0D 50 8D 6A CB 61
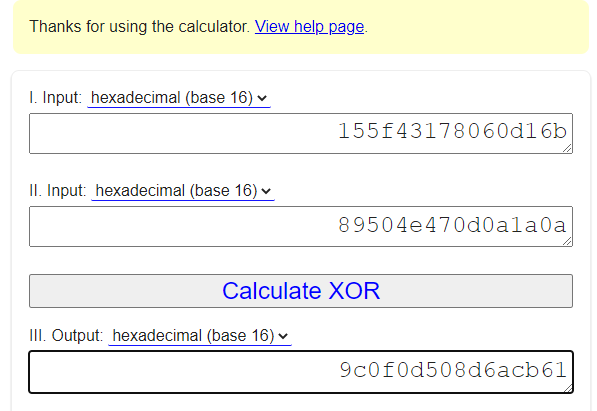
Then XOR the encrypted image with the previous result with cyberchef :3 It shows a correct .png file! lets see what’s inside it.

A Github logo? Im curious if HackLabs have a github account, lets see.
After i visited the Hacklabs’s github account, there’s a folder that contains this challenge flag but it’s a fake flag. Github have some features to see what’s been changed recently.

Flag : HACKLABS{W3_H4v3_a_g1THuB_p4G3_t0_y0U_kN0w}
Is it shredded? - Forensic
Given a “shredded” .jpg file. I tried to unshred the image with Photoshop. After reassembling the shredded image it returns a fake flag :<.
So i found a similar challenge “Warpspeed”. If .jpg is resized it will be “shredded” and if its a .png file it will corrupt the file. *thanks to Felix (he told me after i solved this challenge)
Lets change the image size with hex editor.
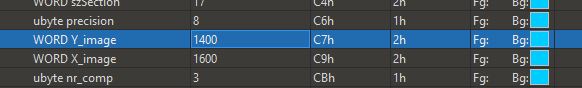
After bruteforcing the image size, i found the flag on the bottom of the image !
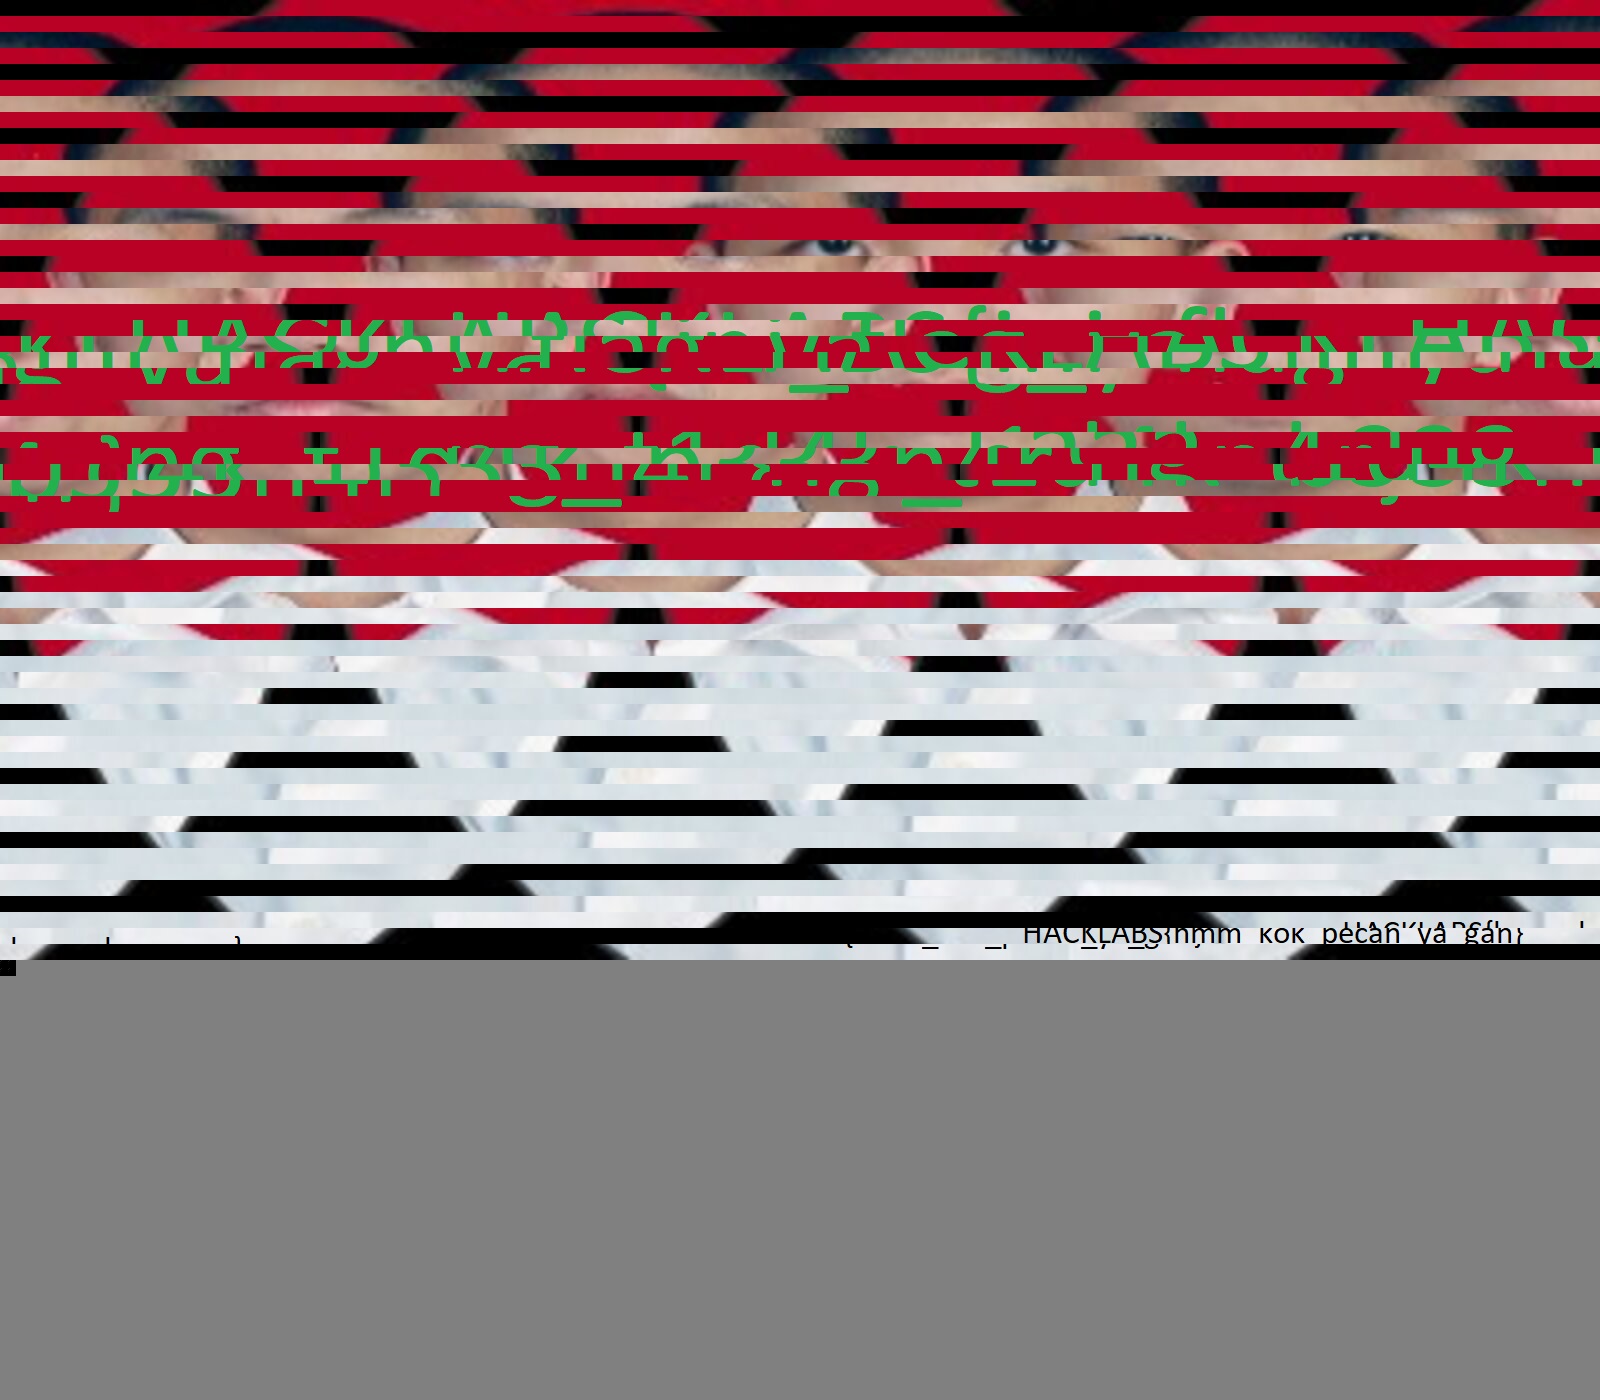
Flag : HACKLABS{hmm_kok_pecah_ya_gan}
Covert Pipe - Forensic
Given .pcap file, I tried to inspect all the protocols that available in this file. ICMP protocol seems good to me, i can see ping request with some data. *I’m inspired by this Writeup
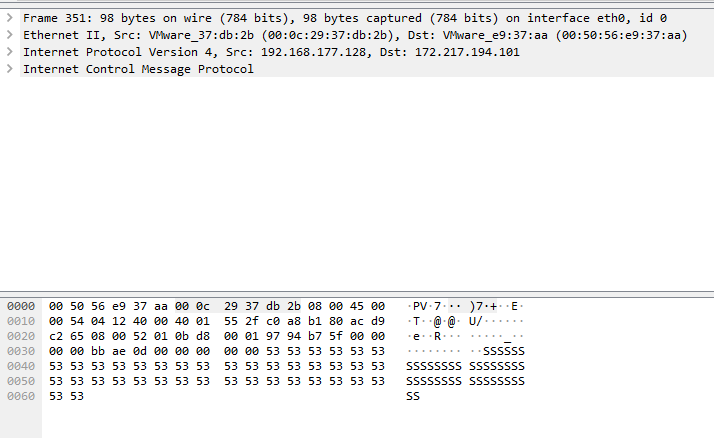
Then i use the script to get the data from ICMP protocol and it returns a Base64 encoded strings, just decode that string with online tools or base64 -d in Linux terminal.

Flag : HACKLABS{icmp_exfiltration_is_annoying}
Truly Antagonist - Misc
Back again with another zip cracking challenge, given a hint that the first password of the first zip is phone number with XL operator (11 digits). Lets make the wordlist with crunch and crack the zip with John.
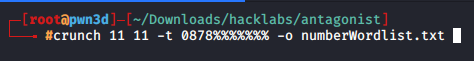

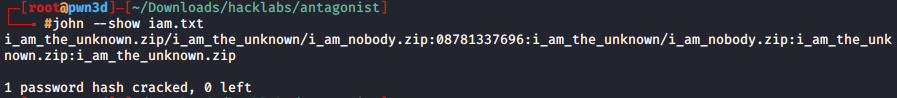
1st zip password : 08781337696
Unzip the 1st zip and i got the 1st part of the flag with hints for cracking the 2nd part.
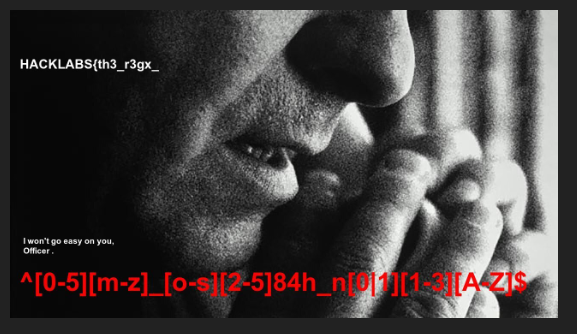
Time to make the wordlist based on regex with exrex.py and repeat the previous steps.

2nd zip password : 3n_s484h_n03R

I got the 2nd part of the flag and the hints, repeat the steps again :c
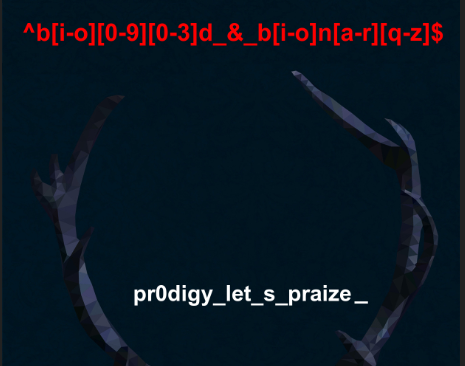

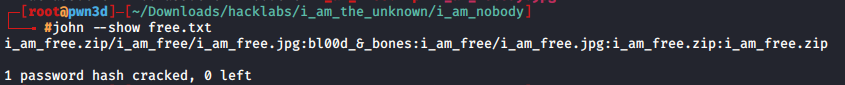
last zip password : bl00d_&_bones
last part of the flag
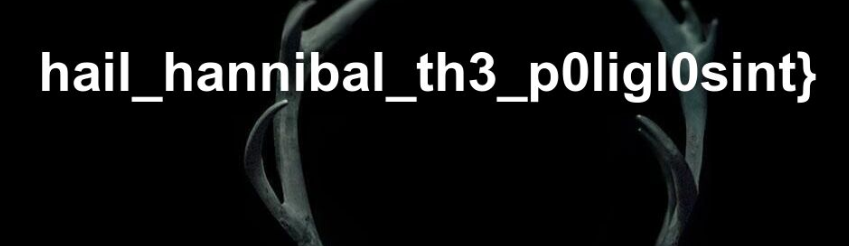
Flag : HACKLABS{th3_r3gx_pr0digy_let_s_praize_hail_hannibal_th3_p0ligl0sint}
That’s all folks. Thank you for the amazing challs and Thank you for reading this writeup! See ya ~